About this publication
Writing on Decagon's security program
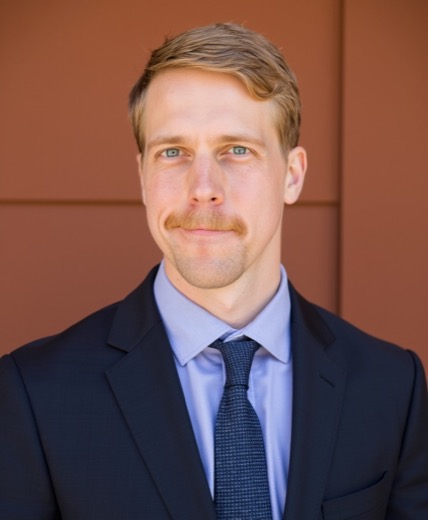
Author
Ben Draffin
Director of Security, GRC and IT at Decagon · San Francisco
I was Director of Security, GRC and IT at Decagon, where the job was making a young AI company credible to sophisticated enterprise buyers. I write here about how that work actually goes.
Before Decagon, I was Senior Staff Security Engineer at Verkada, where I led the company-wide response to an FTC consent order, and spent several years on product security and identity at Box as a founding engineer on Box Shield. CISSP and CISA. MS in Information Security from Carnegie Mellon; B.Eng. from Vanderbilt.
I started this site to write down what I learned on the job: how enterprise deals actually move, where controls lag product, what auditors push on, and what it takes to make a young AI company credible to a careful buyer. Examples are anonymized when they need to be.
I also angel-invest in and advise pre-seed, seed and Series A startups in security, GRC, AI and infrastructure: usually enterprise readiness, security product strategy, and standing up a security and compliance program from nothing. Reach out anytime.
Opinions are mine, not Decagon's.
For security and GRC leads at companies moving up-market, people who already know the frameworks and want to know what actually moves a deal.
Methodology
I write from my time at Decagon: redlines, MSA and DPA negotiation, vendor reviews, auditor interviews, the gap between policy and what engineering can demo. If a post mentions a control or negotiation pattern, it's because I hit it repeatedly, not because a checklist suggested it.
What to expect
- Usually about one post a week
- Long essays, not news roundups
- Deal patterns and tradeoff tables where they help
- No sponsors
Corrections
If I get something wrong, I fix it and add Updated YYYY-MM-DD: at the bottom. Typos get fixed quietly.
Stay in touch
Subscribe to the newsletter , follow me on LinkedIn , or use the RSS feed .